Be ready for the audit before it is announced
Know who did what and when, limit who can do it, and prove the records have not been changed.
Controls auditors ask about
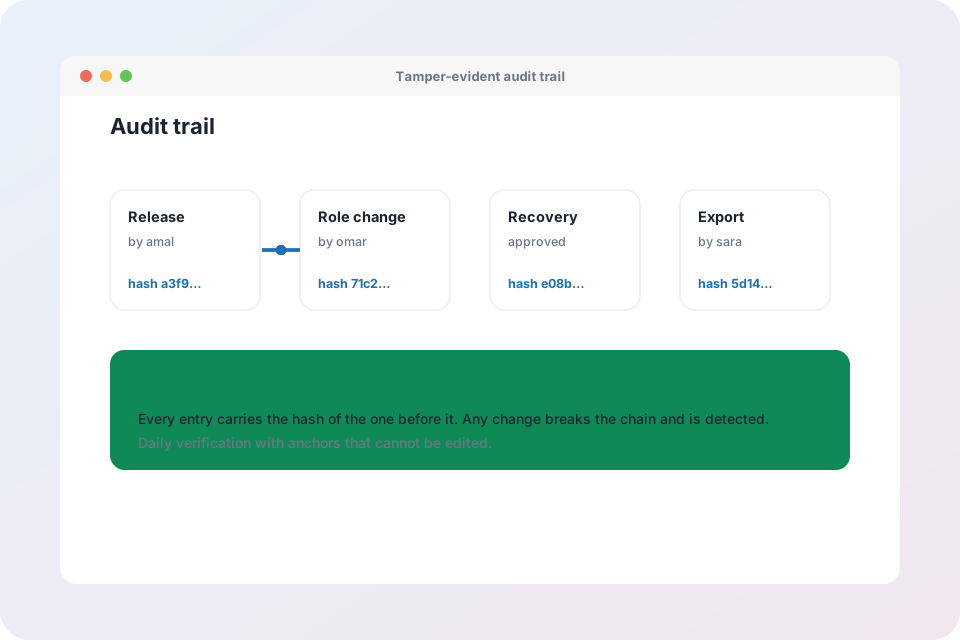
Tamper-evident audit trail
Entries are chained together, so any change or deletion is detected when the log is verified.
Custom roles and rights
Build roles from individual rights so each person can do their job and nothing more.
Step-up two-factor
Sensitive actions such as recovery or policy changes ask for a fresh second factor.
Approval workflows
Requester and approver are always different people.
Retention and legal holds
Keep what you must and delete what you may, with holds that override clean-up.
Searchable and exportable
Filter the audit log by person, action and date and export it for reviewers.
A log you can verify
Each entry carries a fingerprint of the one before it. If a record is edited or removed, verification fails and shows where.
- Covers logins, policy changes, releases and recoveries
- Reasons recorded with sensitive actions
- Verification on demand
Compliance questions
Does X-Protection make me compliant by itself?
No product can. It provides the controls and evidence, such as retention, approvals and an audit trail, that your own compliance process relies on.
Can I create my own roles?
Yes. Combine individual rights into a role, for example a role that can review quarantine but cannot recover mail.
Is two-factor required?
Staff can use it for sign-in, and sensitive actions ask for a fresh code even in an active session.
Make audits routine
Request an account to see the audit trail in action.
Explore X-Protection
- X-Protection overview – every feature on one page
- Spam, malware and link protection – spam rules, reputation, attachment analyzer and URL protection
- X-Trust impersonation defence – BEC and look-alike sender detection with 18 signals
- Archive, legal hold and recovery – encrypted archive, retention and Recovery Desk
- Quarantine, digests and mail trace – release requests, allow and block lists, delivery monitor
- Compliance, audit and access control – tamper-evident audit trail, custom roles and two-factor
- X-Protection for MSPs and resellers – one console for every customer, plans and usage
- Mail Admin – the control panel for business email