Catch the fake boss before the payment goes out
Business email compromise has no virus to detect. X-Trust studies who is really writing and holds the message when something is off.
How X-Trust works
18 trust signals
Display-name tricks, look-alike domains, reply-to mismatches, new senders, urgent payment wording and more.
Learns your real contacts
Knows who normally writes to whom, so a stranger posing as your CEO stands out.
Monitor, review, enforce
Begin by only recording, move to review, then enforce when you trust the results.
Consent and control
Learning from mail is enabled only with your consent, per customer.
Outgoing journal
A record of outgoing mail helps recognise real relationships and review what left your company.
Held, not lost
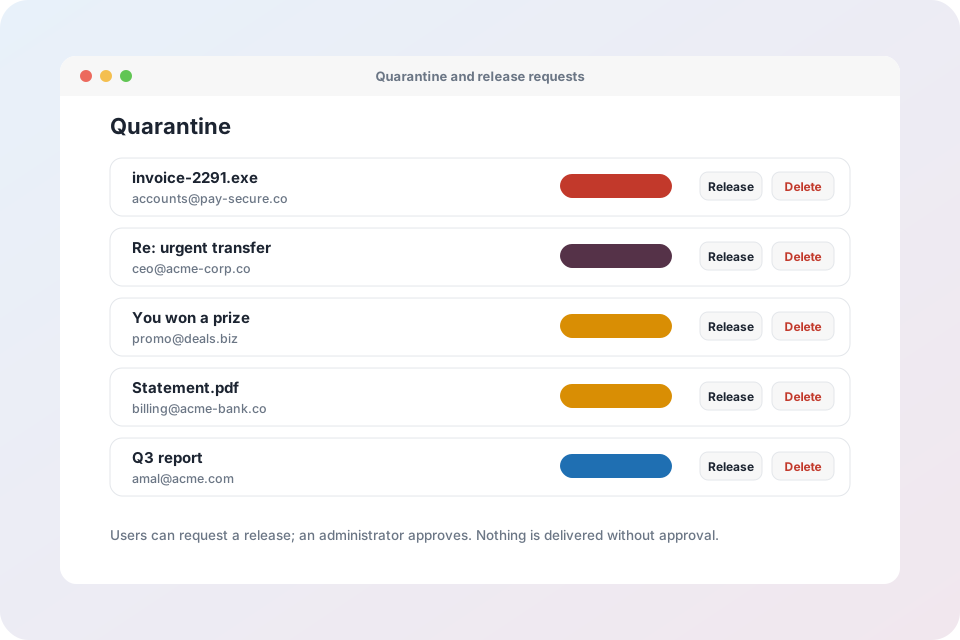
Suspicious messages go to quarantine with the reasons, ready for a quick decision.
Typical attacks X-Trust catches
These attacks look like normal email, which is why filters that only look for viruses miss them.
- A “CEO” asking finance for an urgent transfer
- A supplier whose bank details suddenly change
- A domain that differs from yours by one letter
X-Trust questions
Will X-Trust interrupt normal mail?
Not in monitor mode. It only records. In review mode suspicious mail is held for a person to decide, and enforce mode applies your chosen action automatically.
Why does it need consent?
Learning relationships means analysing mail metadata, so it is switched on only when the customer agrees.
Does it protect against spoofing of my own domain?
Yes. Spoofed senders using your domain are scored together with SPF, DKIM and DMARC results.
Protect the people who handle money
Turn on X-Trust in monitor mode and see what it finds.
Explore X-Protection
- X-Protection overview – every feature on one page
- Spam, malware and link protection – spam rules, reputation, attachment analyzer and URL protection
- X-Trust impersonation defence – BEC and look-alike sender detection with 18 signals
- Archive, legal hold and recovery – encrypted archive, retention and Recovery Desk
- Quarantine, digests and mail trace – release requests, allow and block lists, delivery monitor
- Compliance, audit and access control – tamper-evident audit trail, custom roles and two-factor
- X-Protection for MSPs and resellers – one console for every customer, plans and usage
- Mail Admin – the control panel for business email